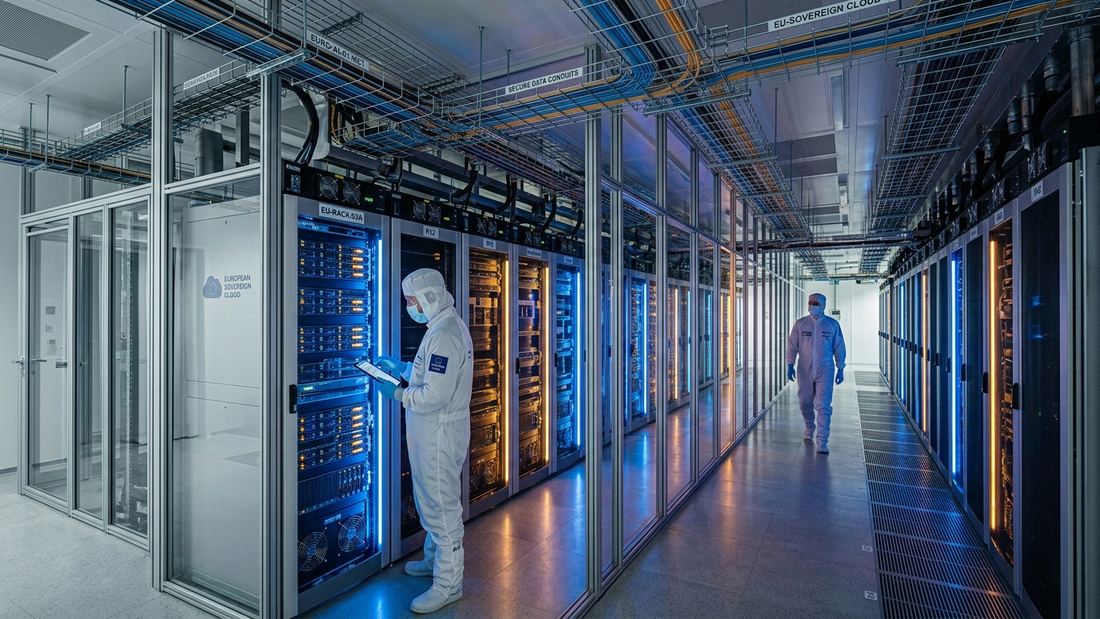
Regulatory & Cloud Architecture Summary
The honeymoon era of borderless cloud AI training is over. With the comprehensive activation of the European Union AI Act, multinational technology giants face an existential operational choice: establish complete operational, physical, and cryptographical sovereignty inside European borders, or face crippling fines reaching up to 7% of global annual turnover.
For over a decade, American cloud hyperscalers treated European data centers as peripheral extensions of their central domestic control planes. Identity services, diagnostic logging, model telemetry, and weights updates routinely traversed transatlantic fiber connections. Under the strict requirements of EU AI Act Article 10 (data governance) and Article 15 (cybersecurity and robustness), that unified architecture is now legally non-compliant.
1. The Anatomy of an EU Sovereign Cloud Enclave
Achieving genuine sovereignty requires far more than spinning up a new availability zone in Frankfurt or Dublin. Sovereign Cloud architecture dictates three mandatory isolation pillars:
- Air-Gapped Identity & Control Planes: European regions cannot rely on US-hosted Active Directory or IAM root tenants. In the event of a total transatlantic network severance, EU enclaves must remain fully operational and manageable.
- EU Citizen-Only Operational Personnel: Physical facility access, hypervisor maintenance, and firmware updates must be executed exclusively by vetted EU nationals residing within the European economic zone.
- Hardware-Enforced Confidential Computing: Model weights and inference prompts must reside within hardware enclaves (Intel TDX, AMD SEV-SNP, or NVIDIA Confidential Computing) where cryptographic keys are managed exclusively by local sovereign key management modules.
2. Architectural Costs and the Sovereign Compute Premium
This regulatory segmentation is introducing what enterprise analysts term the “Sovereign Compute Premium.” Because European data centers must duplicate control plane infrastructure, maintain dedicated local engineering teams, and comply with strict energy and cooling regulations, per-token inference costs inside EU sovereign enclaves are tracking between 22% and 38% higher than equivalent US-based API endpoints.
| Hyperscaler Sovereign Initiative | Primary European Partner | Isolation Mechanism | Compliance Status |
|---|---|---|---|
| AWS European Sovereign Cloud | Dedicated German Entity (Brandenburg) | Independent parent partition & root KMS | Phased Rollout |
| Microsoft Cloud for Sovereignty | National partners (Orange, Capgemini) | Confidential Azure Virtual Machines | Active Deployment |
| Google Cloud Sovereign Solutions | T-Systems (Germany) / Thales (France) | External key management & air-gapped IAM | Active Deployment |
3. The Long-Term Geopolitical Bifurcation
As explored in our investigative audit of OpenAI’s security protocols and government data boundaries, the intersection of autonomous AI runtimes and critical national infrastructure is becoming the defining cybersecurity battlefield of the decade. The EU AI Act is merely the opening salvo in a worldwide trend toward sovereign compute borders, where every sovereign state demands absolute cryptographical control over the intelligence operating within its jurisdiction.
Primary Regulatory Sources & Compliance Standards
The conformity assessment workflows, air-gapped sovereign boundary specifications, and high-risk classification criteria detailed in this framework are based directly on official European Union statutory publications:
- Official EU AI Act Legislation: Regulation (EU) 2024/1689 of the European Parliament and of the Council. “Laying down harmonised rules on artificial intelligence (Artificial Intelligence Act).” Official Journal of the European Union. EUR-Lex Regulation (EU) 2024/1689.
- European AI Office Directives: European Commission Directorate-General for Communications Networks, Content and Technology. “Implementation Guidelines for General-Purpose AI (GPAI) Models and Systemic Risk Evaluation.” European AI Office Portal.
- ENISA Cloud Cybersecurity Framework: European Union Agency for Cybersecurity. “European Cybersecurity Certification Scheme for Cloud Services (EUCS) and Sovereign Data Governance.” ENISA Cloud Guidelines.