A Sovereign AI Cloud is a physically or cryptographically isolated compute infrastructure designed to train, fine-tune, and serve artificial intelligence models entirely within a defined jurisdictional boundary. By enforcing three non-negotiable pillars—Data Sovereignty (zero foreign jurisdiction access), Operational Sovereignty (local administrative control), and Model Sovereignty (ownership of weights and weights provenance)—sovereign AI architectures allow nation-states, defense sectors, and heavily regulated enterprises to achieve frontier intelligence without exposing trade secrets or statutory data to extraterritorial subpoena (such as the US CLOUD Act or FISA Section 702).
Air-Gapped Validated
Confidential Computing
InfiniBand Topology
In 2026, the artificial intelligence industry has arrived at a structural inflection point. While public hyperscaler APIs (OpenAI on Azure, Anthropic on AWS, and Google Cloud Vertex AI) provided unprecedented speed-to-market during the early generative AI wave, their centralized architecture introduces existential risks for sovereign nations and global enterprises. Sending sensitive proprietary datasets, healthcare records, financial ledgers, and government intelligence across public APIs creates unavoidable vulnerabilities around data custody, foreign extraterritorial intercept, and vendor lock-in.
Consequently, organizations and governments worldwide are aggressively investing in sovereign AI cloud infrastructure. This engineering guide details the architectural blueprints, hardware sizing, networking fabrics, and regulatory compliance frameworks required to design and deploy an enterprise-grade sovereign AI cloud.
1. The Tripartite Pillars of Sovereign AI
True sovereign AI cannot be achieved simply by hosting virtual machines in a local availability zone of a foreign public cloud provider. True sovereignty demands end-to-end independence across three distinct operational layers:
- 1. Data Sovereignty: Complete cryptographic and geographical isolation ensuring training datasets, customer prompts, embeddings, and telemetry logs never cross national borders or enter foreign-controlled cloud fabrics.
- 2. Operational Sovereignty: Data centers, hardware supply chains, and cluster orchestration must be operated by citizens or security-cleared personnel holding local allegiance, preventing remote kill-switches or forced administrative overrides.
- 3. Model & Software Sovereignty: Full access to model weights, fine-tuning artifacts, and inference engines (e.g., Llama 3.3, Mistral Large, DeepSeek, Qwen) without external licensing telemetry, ensuring continuous mission viability even during geopolitical trade embargoes.
2. Three Architectural Blueprints for Sovereign Deployments
| Deployment Blueprint | Network Isolation Level | Hardware Enclave Model | Primary Use Case | Typical Latency & SLA |
|---|---|---|---|---|
| Blueprint A: Full Air-Gapped Vault | 100% Zero-Egress (No Internet) | Bare-metal on-premises GPU clusters | Defense, intelligence, critical energy grids | Sub-2ms internal LAN SLA |
| Blueprint B: Confidential Enclave Cloud | VPC with Hardware TEE Encryption | AMD SEV-SNP / NVIDIA H100 CC | Banking, healthcare, HIPAA/GDPR clinical AI | 5 – 12ms regional TLS SLA |
| Blueprint C: Sovereign Federated Mesh | Encrypted Inter-Node Tunneling | Decentralized edge nodes + Central aggregator | National hospital networks, cross-border research | Asynchronous gradient sync |
Blueprint A: The Zero-Egress Air-Gapped Vault
In the air-gapped topology, the GPU training and inference clusters have zero physical connection to public internet routing tables. Internal model registry updates and weights ingest are executed via hardware unidirectional data diodes (such as Owl Cyber Defense or Advenica) that enforce one-way optical transmission. Package repositories (Python PyPI, Docker images, Hugging Face models) are maintained as locally verified, vulnerability-scanned offline mirrors.
Blueprint B: Confidential Cloud Enclaves
For commercial enterprises seeking cloud elasticity without sacrificing sovereignty, Confidential Computing provides cryptographic protection. By utilizing AMD SEV-SNP (Secure Encrypted Virtualization) alongside NVIDIA H100 Confidential Computing mode, data in use (in GPU HBM3 memory and CPU registers) remains hardware-encrypted. Even if an adversary compromises the host operating system, hypervisor, or cloud provider administrator credentials, the encryption keys reside strictly within the hardware root of trust, rendering the data completely unreadable.
3. Hardware Topology & Interconnect Sizing
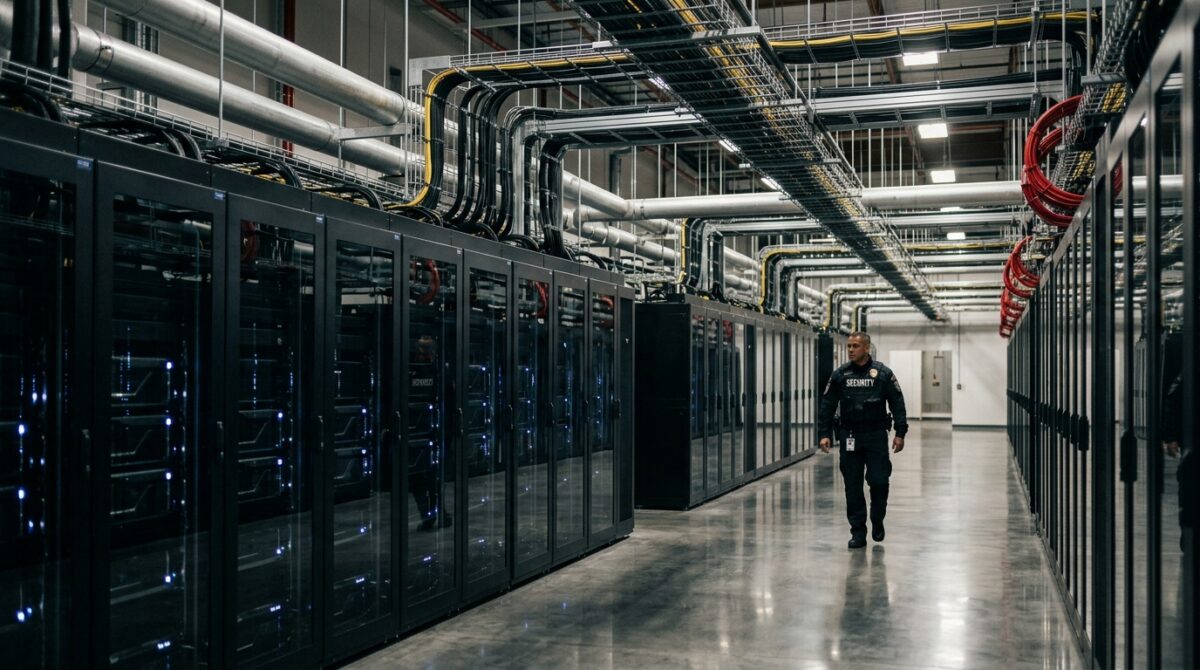
Building an enterprise sovereign AI cluster requires balancing compute density, high-bandwidth memory (HBM), and non-blocking networking fabrics. Below is the standard Bill of Materials (BOM) for a modular 64-GPU sovereign AI pod:
- Compute Nodes: 8x NVIDIA HGX H100/H200 nodes (8x GPUs per node, 141GB HBM3e per GPU), delivering 32 PetaFLOPS of FP8 tensor compute per chassis.
- Intra-Node Interconnect: NVLink 4 delivering 900 GB/s bi-directional GPU-to-GPU bandwidth, enabling seamless tensor parallel execution across all 8 GPUs.
- Cluster Fabric (Scale-Out): Non-blocking NVIDIA Quantum-2 InfiniBand (NDR 400Gb/s) in a rail-optimized 2-tier Fat-Tree topology. For Ethernet-first deployments, RoCEv2 (RDMA over Converged Ethernet) with explicit congestion notification (ECN) and Priority Flow Control (PFC) is mandatory to eliminate packet loss during all-reduce synchronization.
- Parallel Storage Layer: All-NVMe parallel storage (Lustre, WEKA, or Pure Storage FlashBlade) capable of sustaining a minimum of 2.5 TB/s read throughput to ensure massive checkpoint saves and dataset streaming never bottleneck GPU compute cores.
4. Regulatory & Statutory Compliance (EU AI Act & Beyond)
Deploying sovereign AI infrastructure directly addresses stringent international data protection and AI governance mandates:
Statutory Conformity Highlights:
• EU AI Act (Regulation EU 2024/1689) conformity standards: Sovereign infrastructure satisfies strict data governance rules (Article 10) requiring training and validation datasets to undergo rigorous bias and lineage verification under full domestic custody.
• GDPR Chapter V Compliance: Completely circumvents the complexities of cross-border data transfers and standard contractual clauses (SCCs) following Schrems II court rulings.
• ISO/IEC 42001 & ENISA EUCS: Provides physical and cryptographic auditing telemetry proving operational boundaries meet sovereign cloud security certification requirements.
Primary Regulatory Sources & Infrastructure References
The sovereign topologies, security attestation protocols, and statutory compliance baselines cited in this architectural framework originate from official regulatory directives and industry cloud standards:
- European AI Act Statutory Framework: Regulation (EU) 2024/1689 of the European Parliament and of the Council. EUR-Lex Regulation (EU) 2024/1689.
- ENISA Sovereign Cloud Security Guidelines: European Union Agency for Cybersecurity. “European Cybersecurity Certification Scheme for Cloud Services (EUCS) and Sovereign Data Governance.” ENISA Cloud Guidelines.
- Confidential Computing Architecture: Confidential Computing Consortium (Linux Foundation). “Hardware-Based Trusted Execution Environments for High-Performance Workloads.” confidentialcomputing.io.